The CTO’s Guide to Onboarding External Engineering Teams in Under 48 Hours
BLUF Summary: Onboarding external engineering talent into your agency in under 48 hours requires automating identity and permissions provisioning while strictly decoupling legacy environments. By utilizing standardized GitHub teams, automated CI/CD branch protections, and strict environment-variable boundaries, engineering leaders can eliminate onboarding lag and protect core intellectual property.
The Core Agency Bottleneck
When scaling digital agencies through external white-label development partners, the primary point of friction is rarely talent capability—it is operational latency. Most technical directors rely on ad-hoc access requests, manual Slack invitations, and sprawling permission matrices that take weeks to stabilize. This manual friction introduces critical vulnerabilities: orphaned access tokens, insecure direct database connections, and prolonged time-to-first-commit.
For high-velocity agencies managing complex stacks—such as enterprise PHP OOP frameworks or high-throughput MySQL architectures—a fragmented onboarding pipeline directly damages sprint velocity. When external developers wait days for proper staging credentials or secure SSH keys, agile velocity drops and client milestones are immediately compromised.
| Onboarding Method | Provisioning Time | Security Risk Level | Administrative Overhead |
|
Ad-Hoc Manual Setup |
$3\text{ to }5\text{ Days}$ |
High (Orphaned tokens, broad access) |
High (Continuous manual intervention) |
|
Shared Credentials |
Immediate |
Critical (Zero auditing/traceability) |
Low (Until a breach occurs) |
|
Automated Protocol |
$< 48\text{ Hours}$ |
Low (Least-privilege RBAC enforced) |
Minimal (Infrastructure-as-Code) |
Technical & Operational Architecture
To achieve a sub-48-hour onboarding window without compromising security, your agency must enforce a zero-trust boundary around production and staging infrastructure. External engineers should never touch raw production environments or interact directly with live databases.
Instead, architecture must be segmented across distinct layers:
-
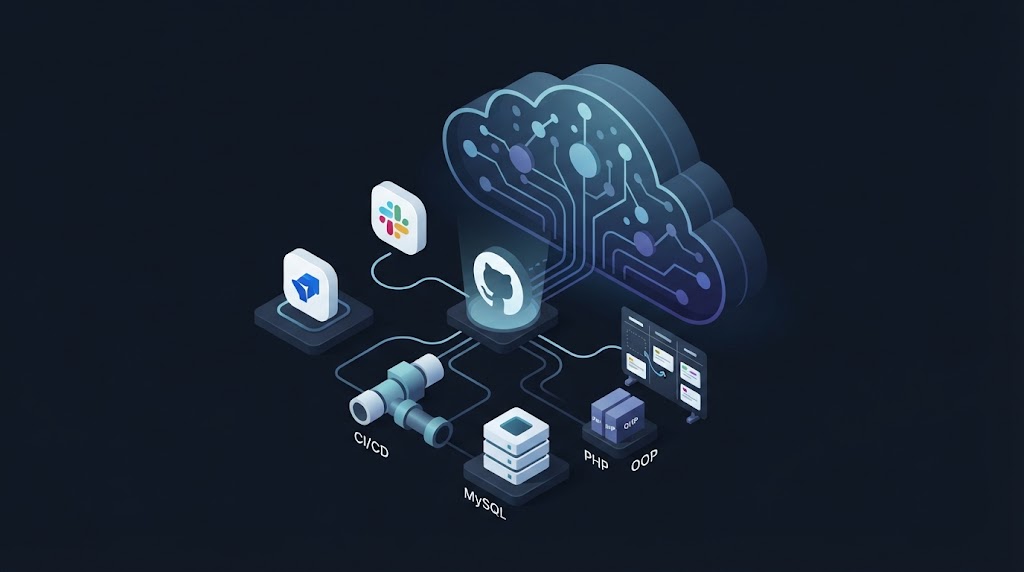
Version Control (GitHub): Access governed by fine-grained Personal Access Tokens (PATs) and organization-level SAML single sign-on. Repositories must enforce branch protection rules prohibiting direct pushes to
mainorstaging. -
Execution Environments: Ephemeral development containers running via Docker Compose, mirroring production PHP engines (e.g., PHP 8.2+ strict types) and database topologies (MySQL 8.0 with InnoDB optimization).
-
Communication & Ticketing (Slack/Jira): Provisioned via automated SCIM (System for Cross-domain Identity Management) provisioning, assigning developers strictly scoped channel access and role-based Jira project filters.
Step-by-Step Execution Protocol
Execute this linear protocol to transition external squads from contract signing to first-commit deployment within 48 hours.
-
Hour 0–12: Identity & Access Management (IAM) Provisioning
-
Enforce hardware-backed multi-factor authentication (MFA) across all identity providers.
-
Integrate the external team into your directory service using SCIM to auto-provision locked-down Slack workspaces and Jira boards.
-
Issue restricted GitHub organization invitations mapped strictly to repository teams (e.g.,
agency-core-backend).
-
-
Hour 12–24: Environment & Secrets Bootstrap
-
Distribute encrypted environment configuration files using secure vault managers (such as HashiCorp Vault or GitHub Actions Secrets) rather than plain-text files.
-
Require developers to spin up standardized local environments using containerized setups. For instance, verify that their local PHP OOP dependency injection containers and MySQL database seeders pass validation tests:
docker-compose up -d --build php vendor/bin/phpunit -
Verify that direct MySQL access is blocked externally and routed exclusively through secure SSH tunnels or internal VPN gateways.
-
-
Hour 24–48: CI/CD Pipeline Handshake & First PR
-
Mandate that external engineers submit a trivial "Hello World" pull request to a sandbox branch.
-
Verify that automated GitHub Actions workflows successfully trigger static analysis tools (e.g., PHPStan level 8), linting scripts, and automated test suites before code review.
-
Once the sandbox PR passes automated quality gates, merge code to staging, confirming full integration loop closure.
-
Continue Reading

Navigating Time-Zone Alignment with Distributed White-Label Development Teams
Preparing Your Agency's Tech Infrastructure for Q4 High-Volume Traffic